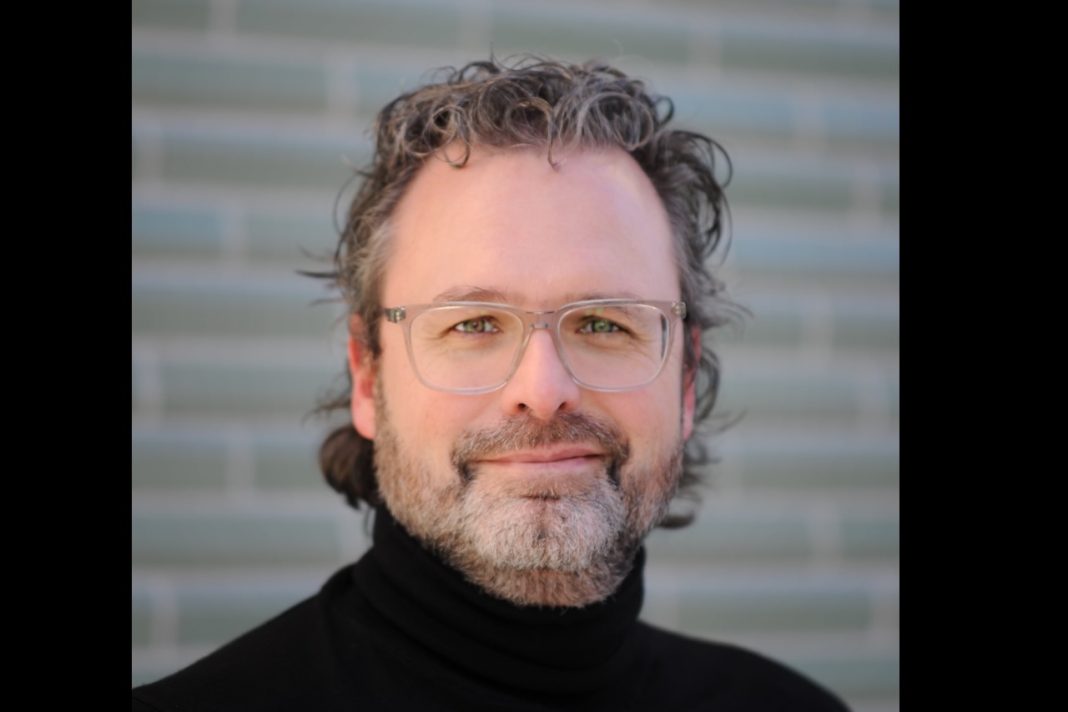
Cyber security failures in business are rarely caused by a lack of technology. Most organisations already have extensive security tooling in place. According to experienced Chief Information Security Officer (CISO), Amy Lemberger, founder of The CISO Hub, the real issue is far more basic: no one senior is clearly owning the decisions that matter.
In many businesses, cyber security still sits under IT, compliance, or procurement. It’s still seen as a ‘nice to have’ and not a ‘must have’. That structural choice shapes how risk is handled. Security becomes operational rather than strategic. Decisions are pushed down the organisation, while accountability remains unclear. When incidents occur, leadership is often caught off guard, despite months or years of warning signs.
Lemberger, a former FTSE-250 CISO who has spent over 17 years working in cyber security, says this misunderstanding is widespread.
“Accountability for cyber risk never leaves the CEO,” she says. “You can delegate responsibility, but you can’t outsource accountability.”
Lemberger argues that hiring a CISO is often misunderstood as a solution in itself. In reality, it changes the quality of information available to leadership, not the level of risk.
“Hiring a CISO doesn’t make risk disappear,” she says. “It makes risk visible. What matters is what the business chooses to do with that visibility.”
Cyber risk, she explains, is not a technical problem that can be solved once and moved on from. It is a continuous series of trade-offs between security, speed, cost, and growth. Those trade-offs sit squarely at leadership level.
When security is buried too far down the organisation, the people closest to the risk often lack the authority to influence outcomes. At the same time, senior leaders may not have a clear or honest picture of the risks they are accepting. The result is a gap that no amount of tooling or policy can close.
Debates about where the CISO should report are common. Should the role sit under the CIO, the CFO, or directly with the CEO. Lemberger believes the reporting line matters less than access and influence.
A security leader who cannot speak directly and plainly to senior decision-makers ends up producing reports that circulate without changing behaviour. A security leader with authority, access, and judgement becomes part of how the business makes decisions.
This disconnect helps explain why many organisations continue to struggle despite sustained investment. Policies exist. Frameworks are referenced. Dashboards are produced. Yet the fundamental question is never properly addressed. What level of risk is the organisation knowingly accepting, and why.
Boards and executive teams do not need deeper technical detail. They need clarity. What is being protected. What could realistically go wrong. What would the impact be. What is being deprioritised, and on what basis.
Treating cyber security as an IT problem creates a false sense of control. Treating it as a leadership responsibility creates accountability. According to Lemberger, organisations that make that shift often move faster, because decisions stop bouncing between teams and start being owned.